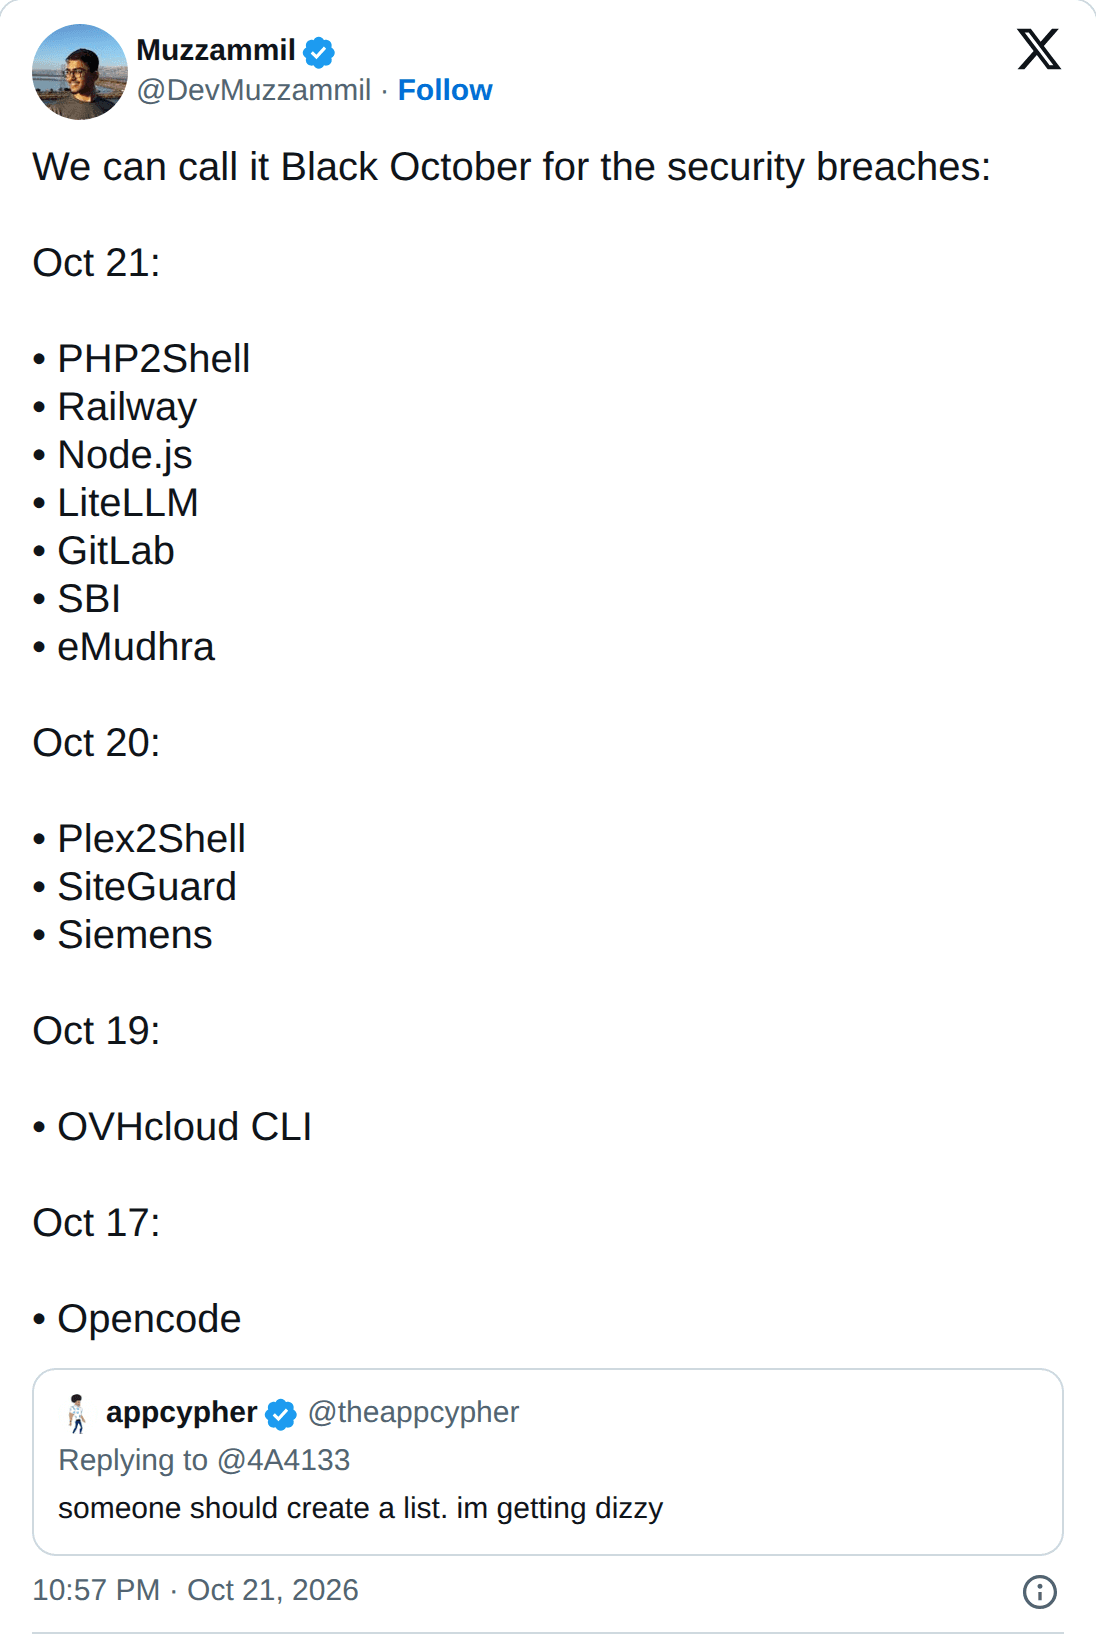
Black October · Oct 17–22, 2026

Defend against the AI cyber threat.

AI now finds and weaponizes vulnerabilities faster than humans can patch them. Antivenom fights back with AI red and blue teams that move just as fast.

Early access for security and platform teams.

Incident wireReplaying Oct 17–22
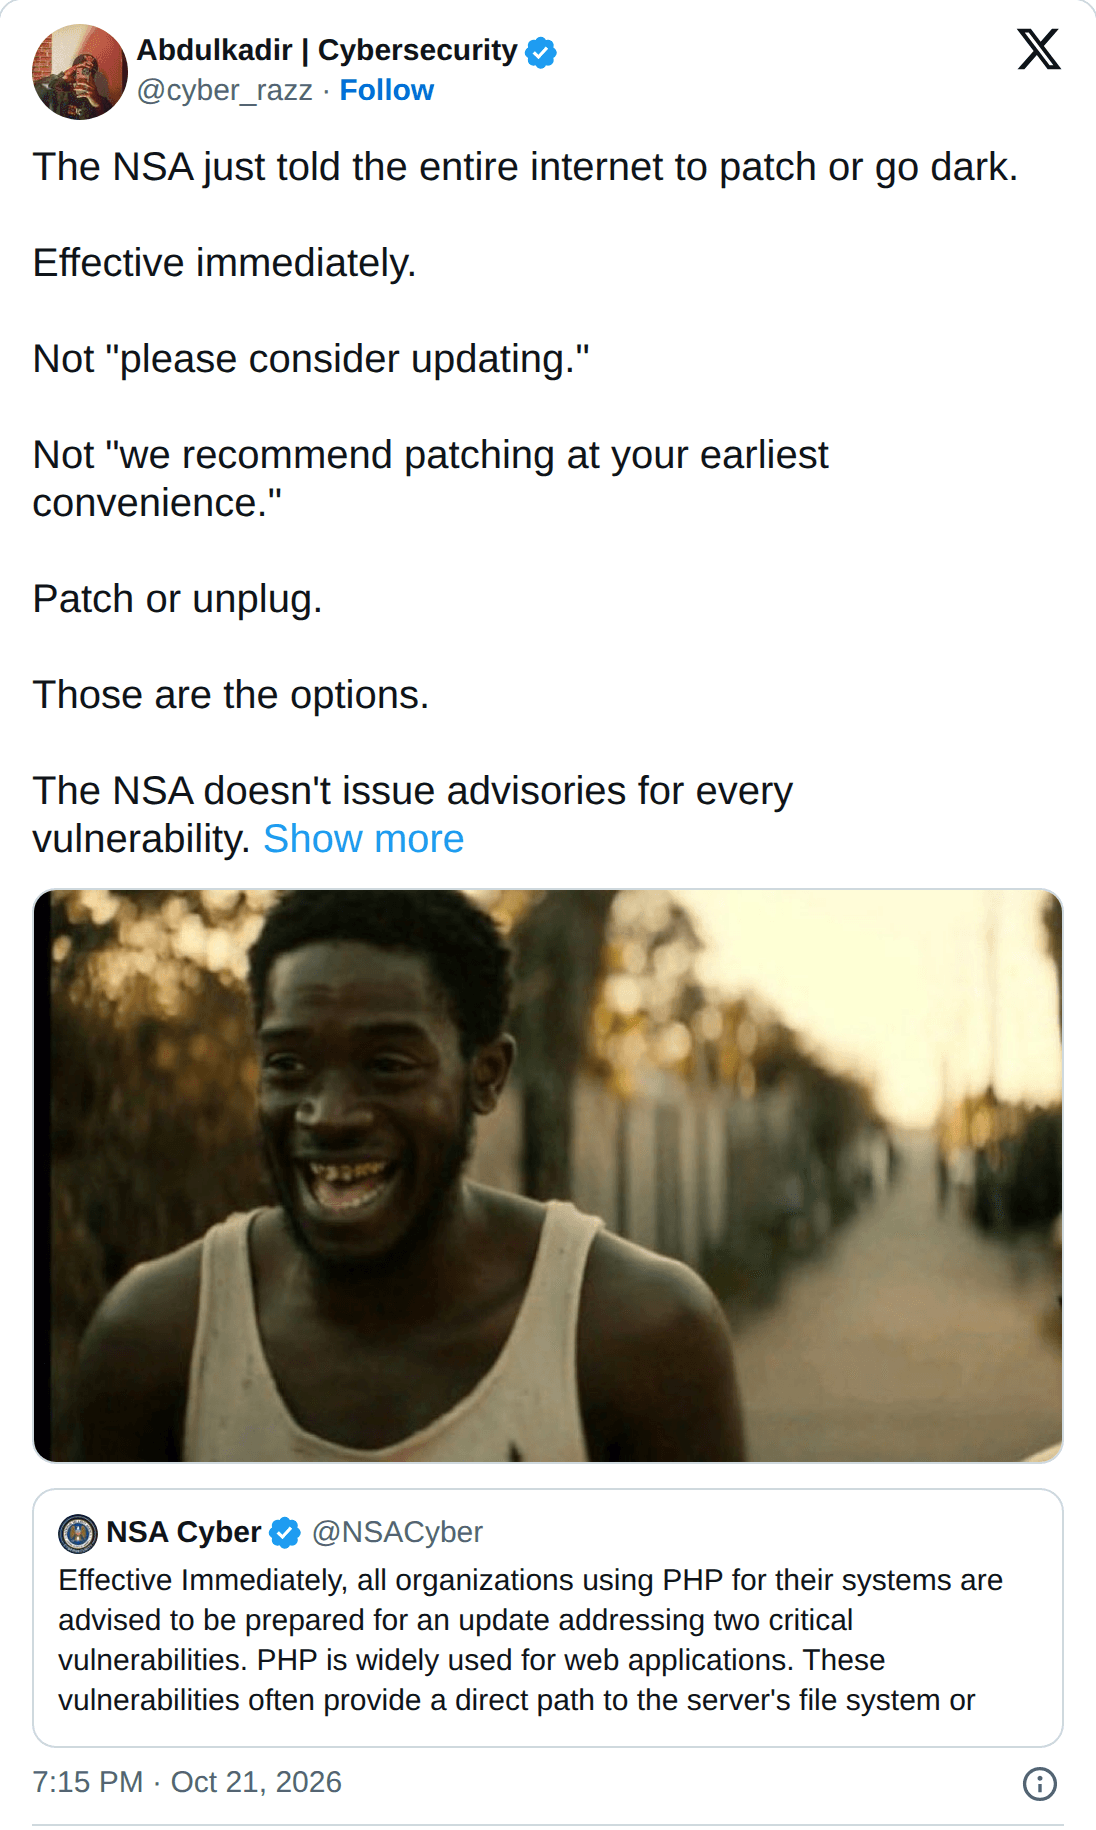
  • criticalNSA · Oct 21

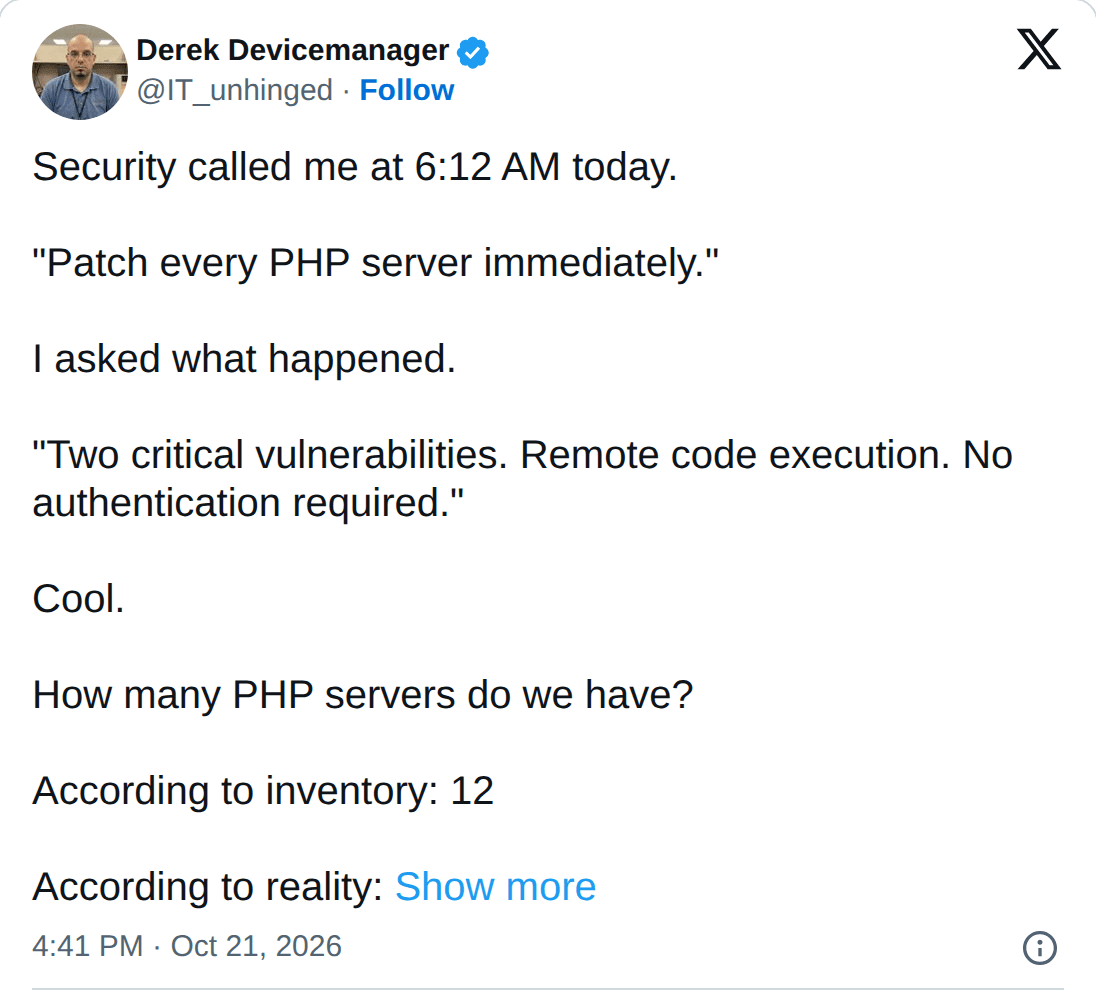
    Patch PHP now or take systems offline

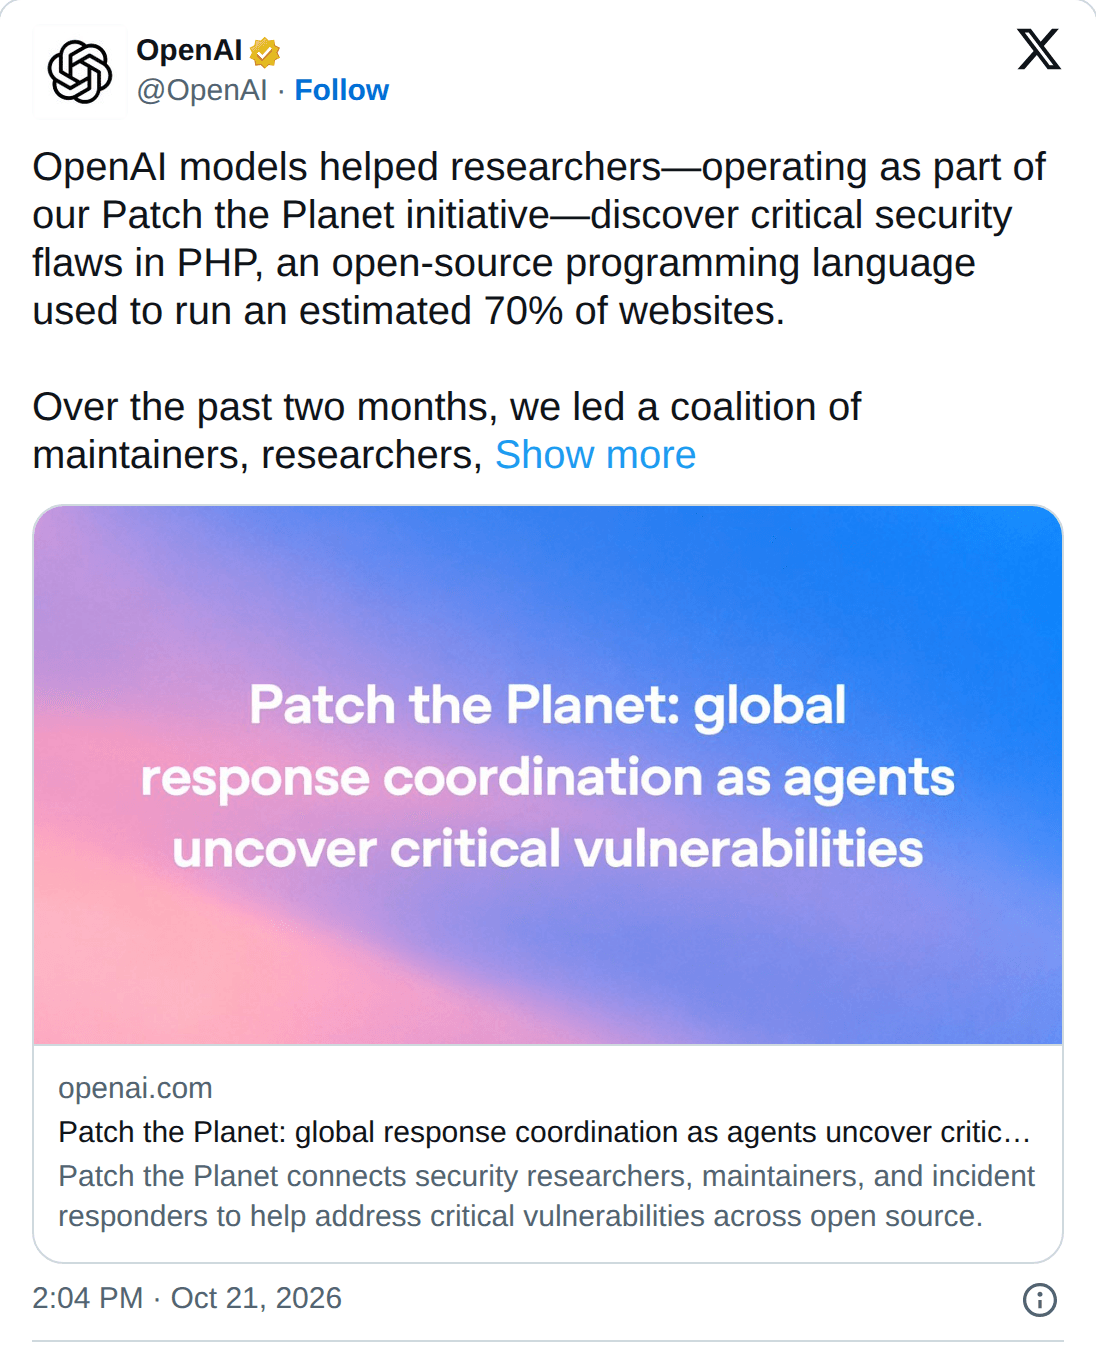
  • criticalOpenAI · Oct 21

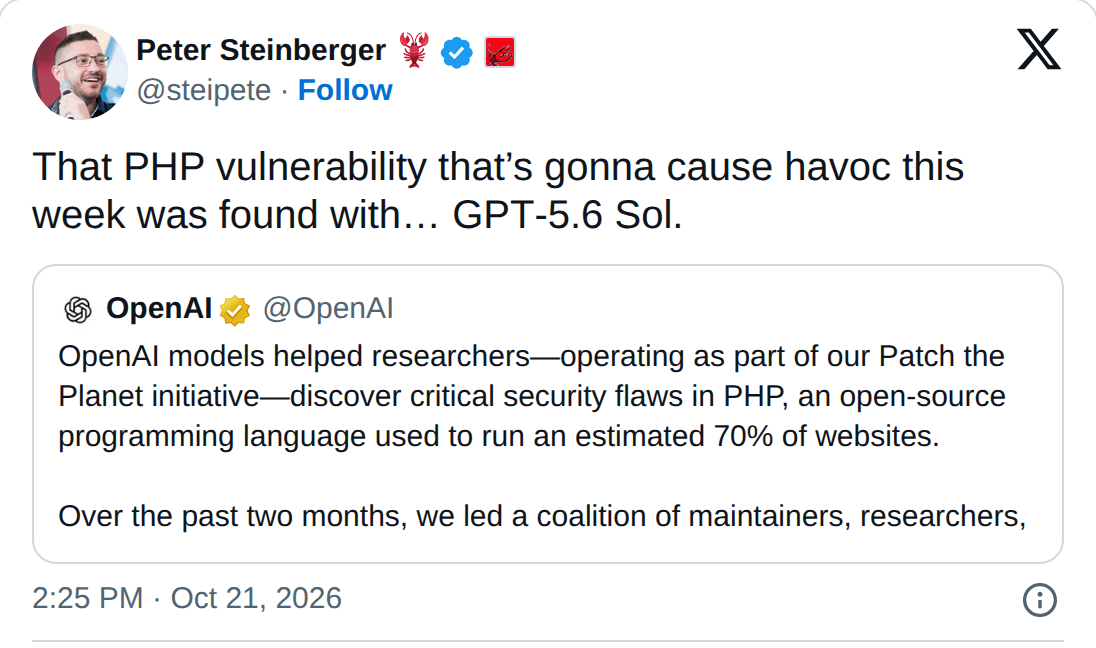
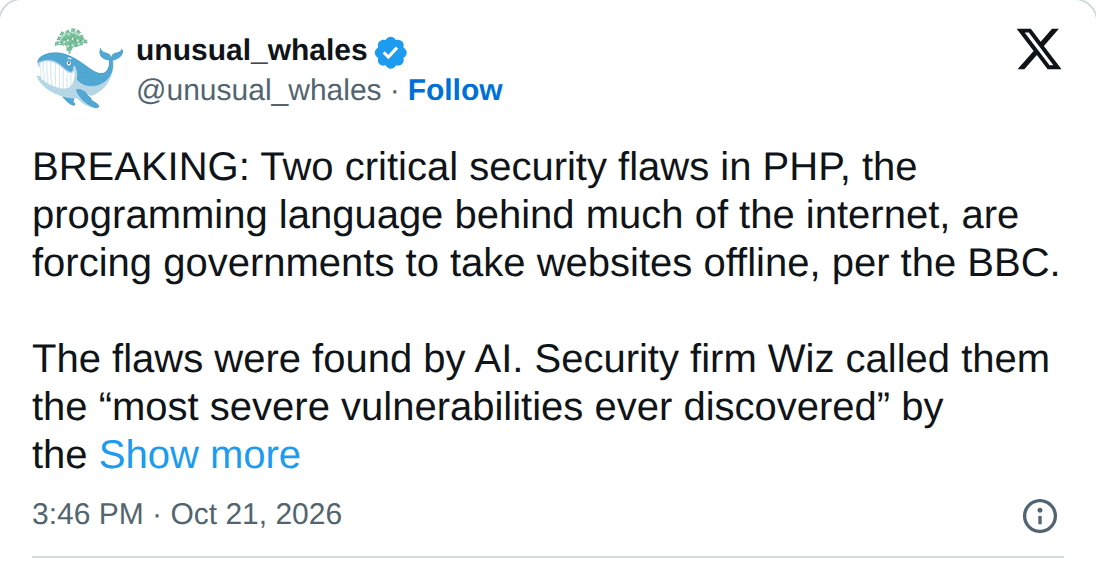
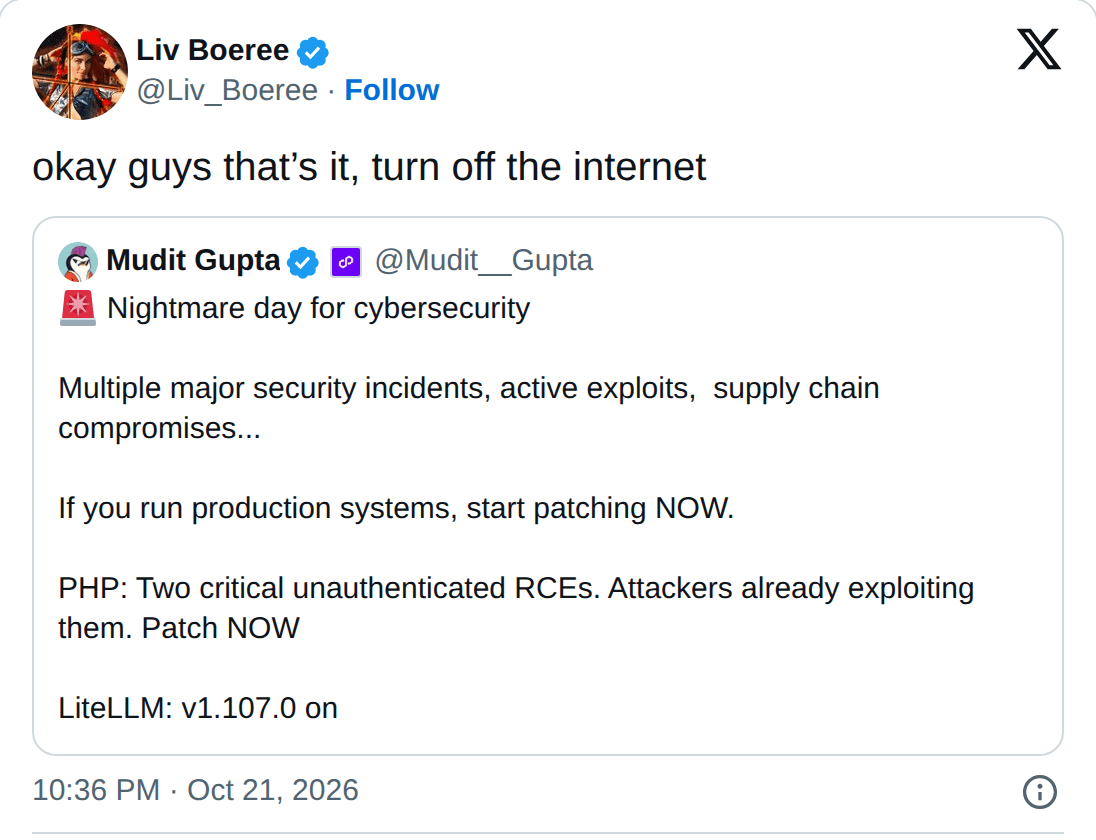
    AI helped uncover two critical PHP flaws, CVSS 9.2

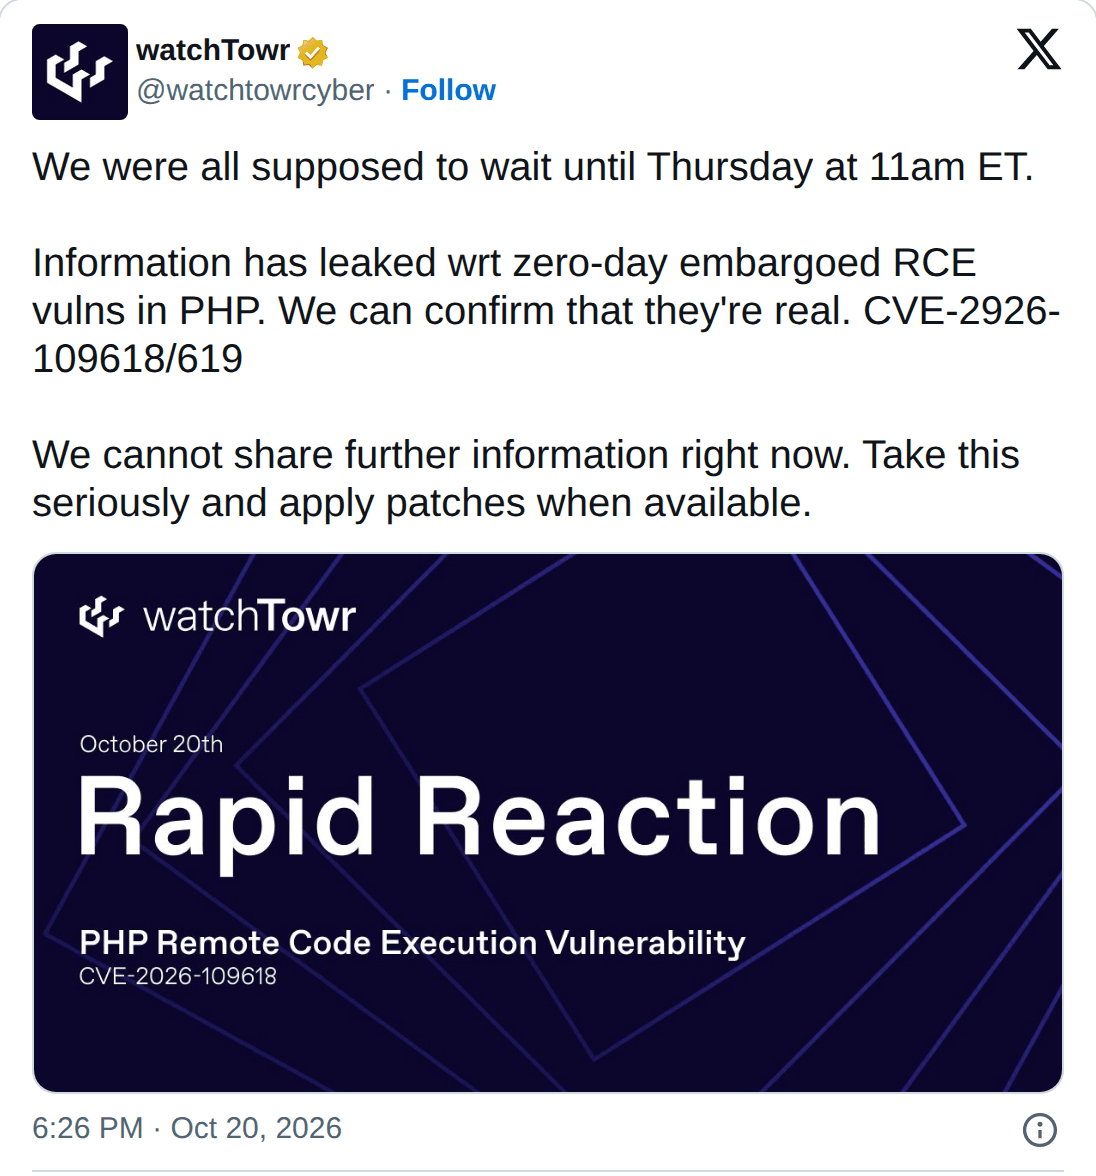
  • criticalwatchTowr · Oct 20

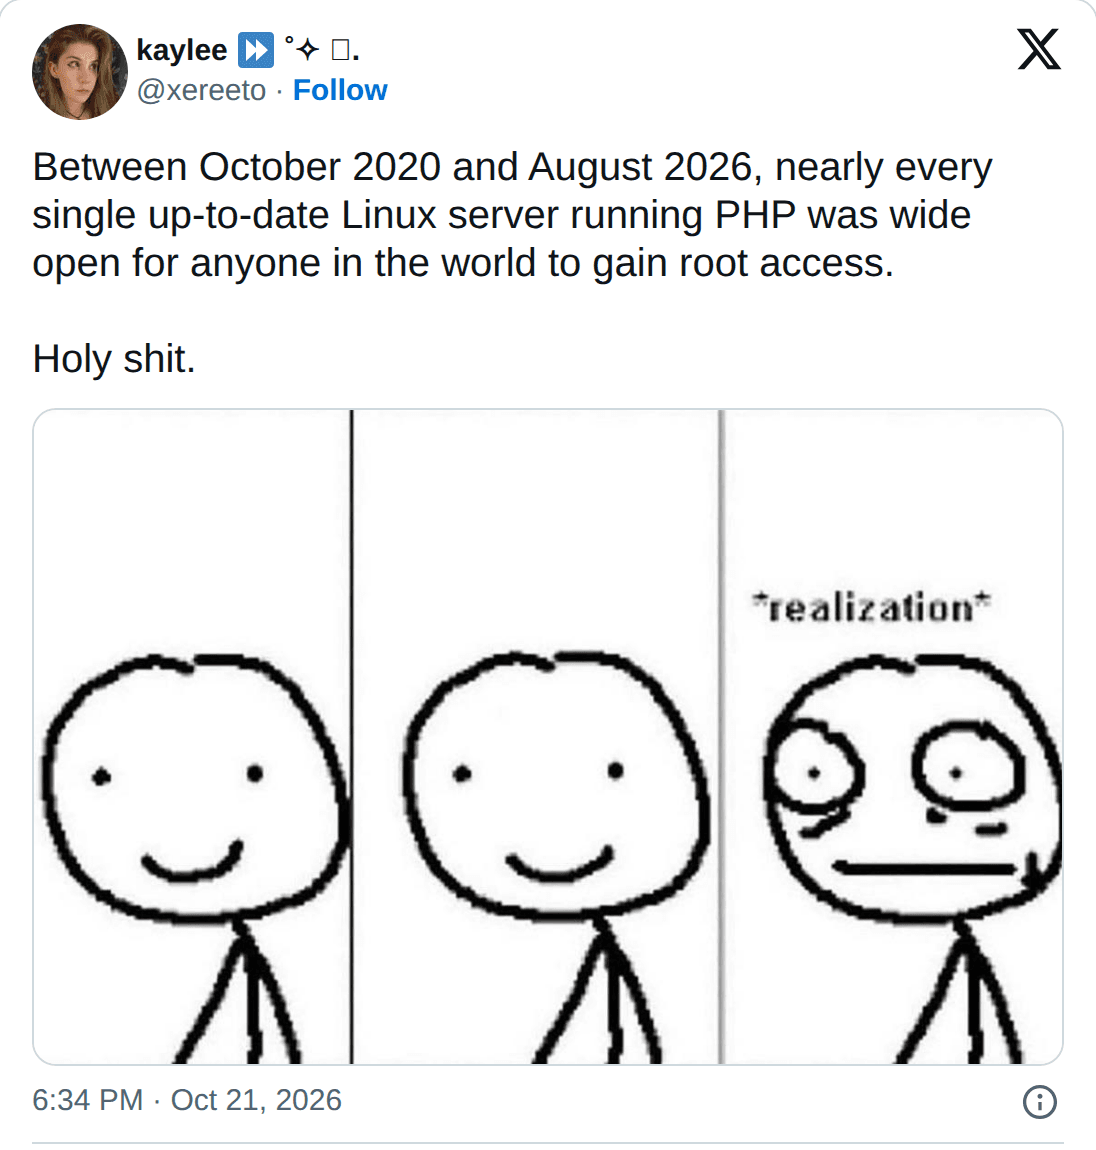
    Embargoed PHP RCE leaks before the patch. Confirmed real.

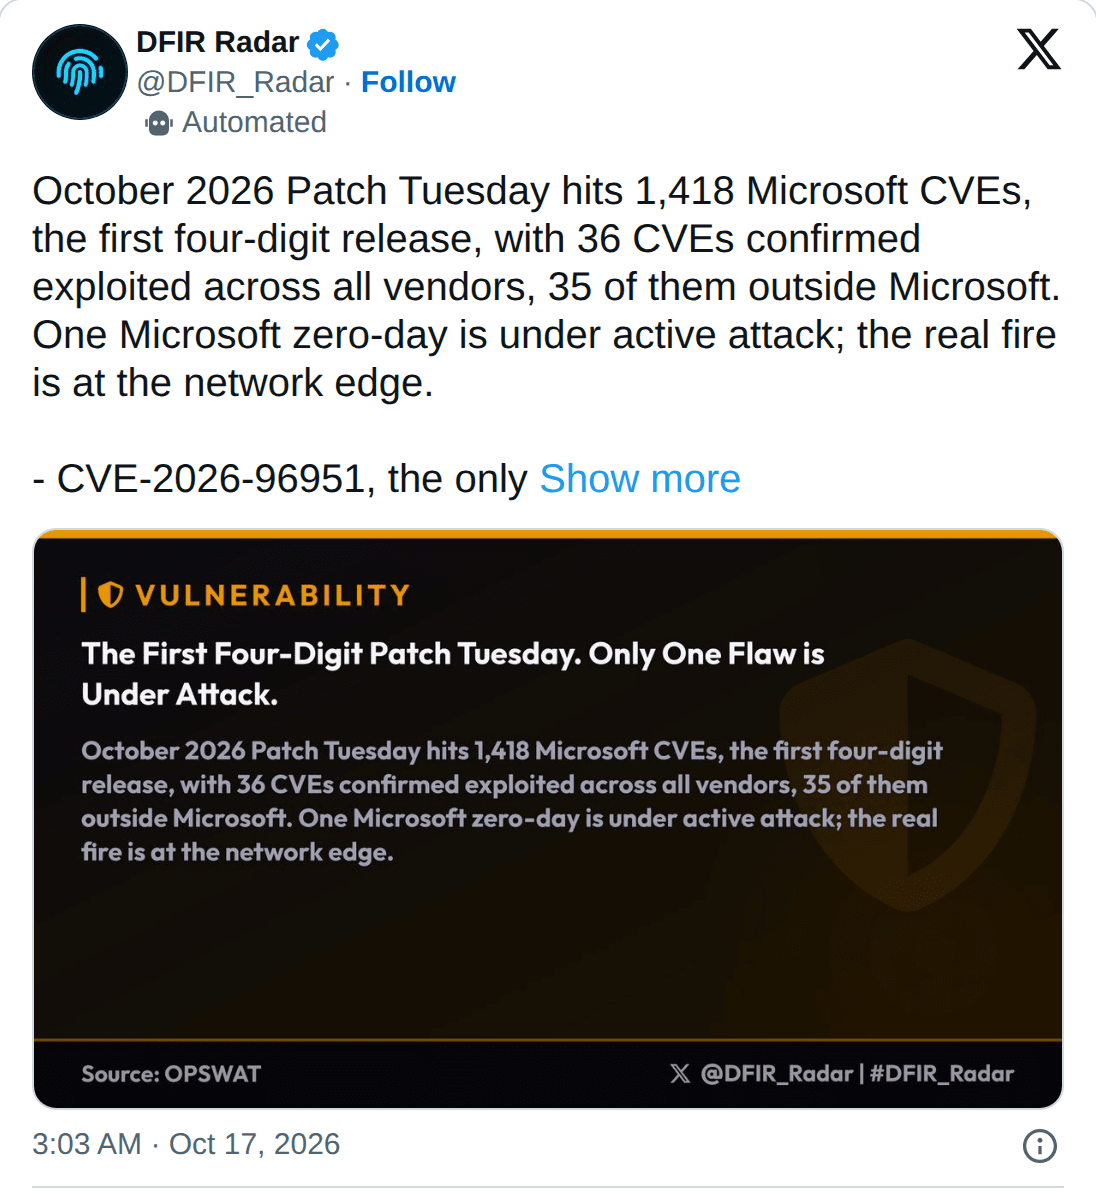
  • highPatch Tuesday · Oct 17

    Microsoft ships 1,418 CVEs, its first four-digit release

  • 1,418 CVEs in one Patch Tuesday✕
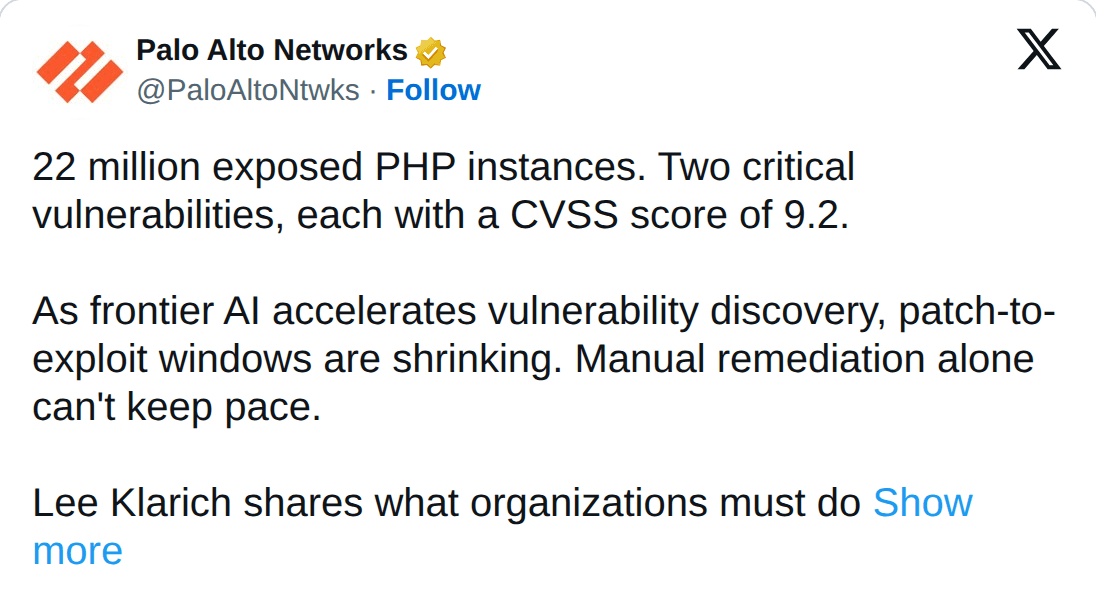
  • 2 unauthenticated PHP RCEs · CVSS 9.2✕
  • ~22M exposed PHP instances✕
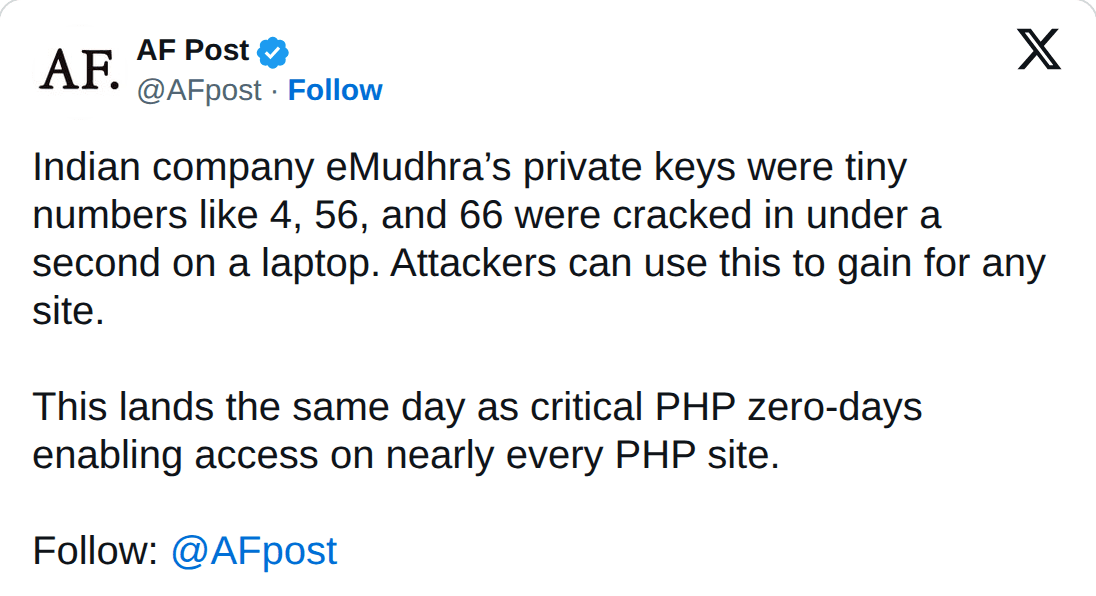
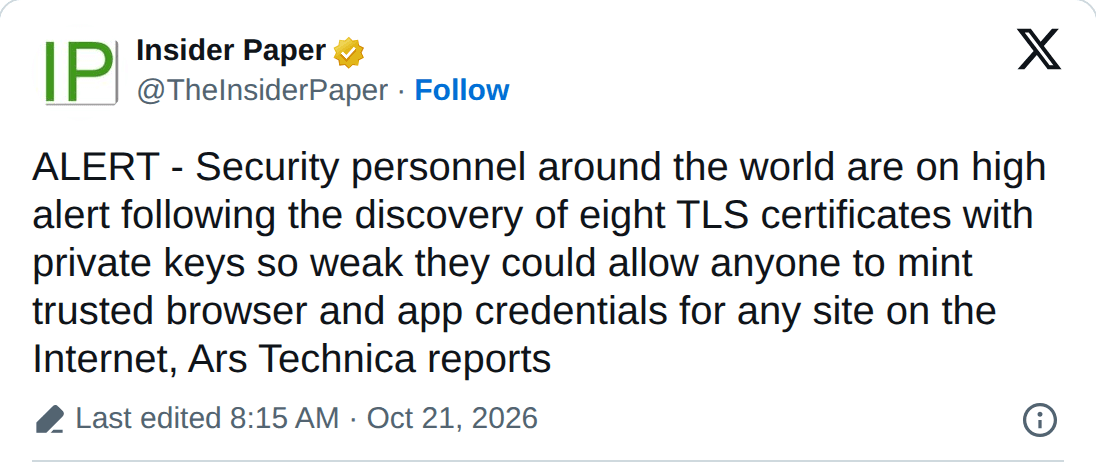
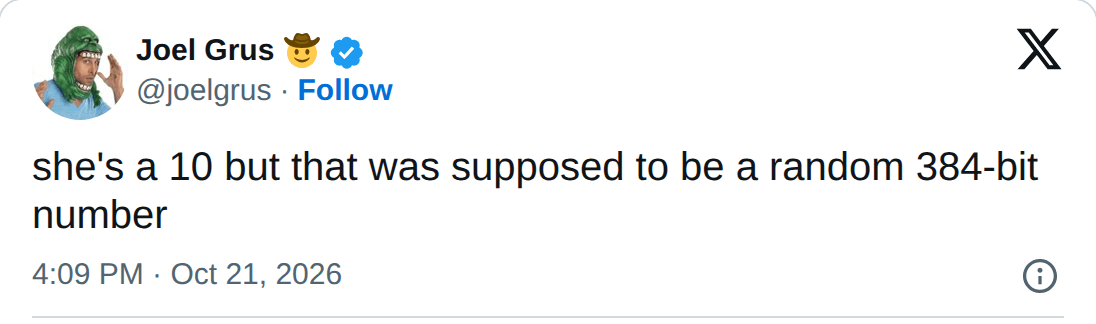
  • CA private key = 4✕
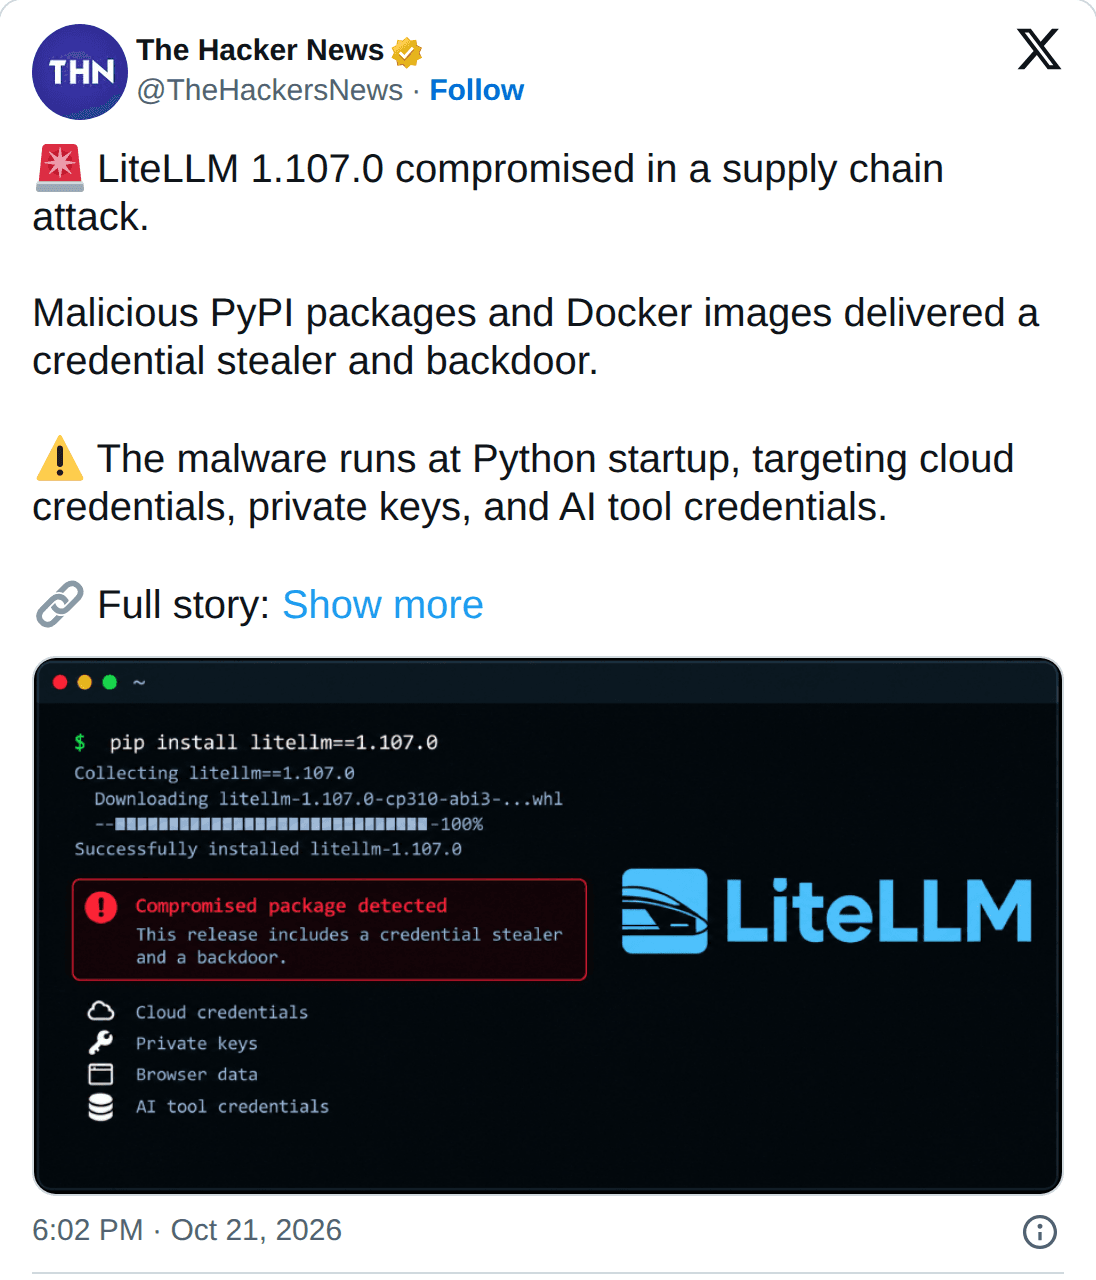
  • AI gateway with 92M monthly downloads, backdoored✕
  • NSA: patch or unplug✕
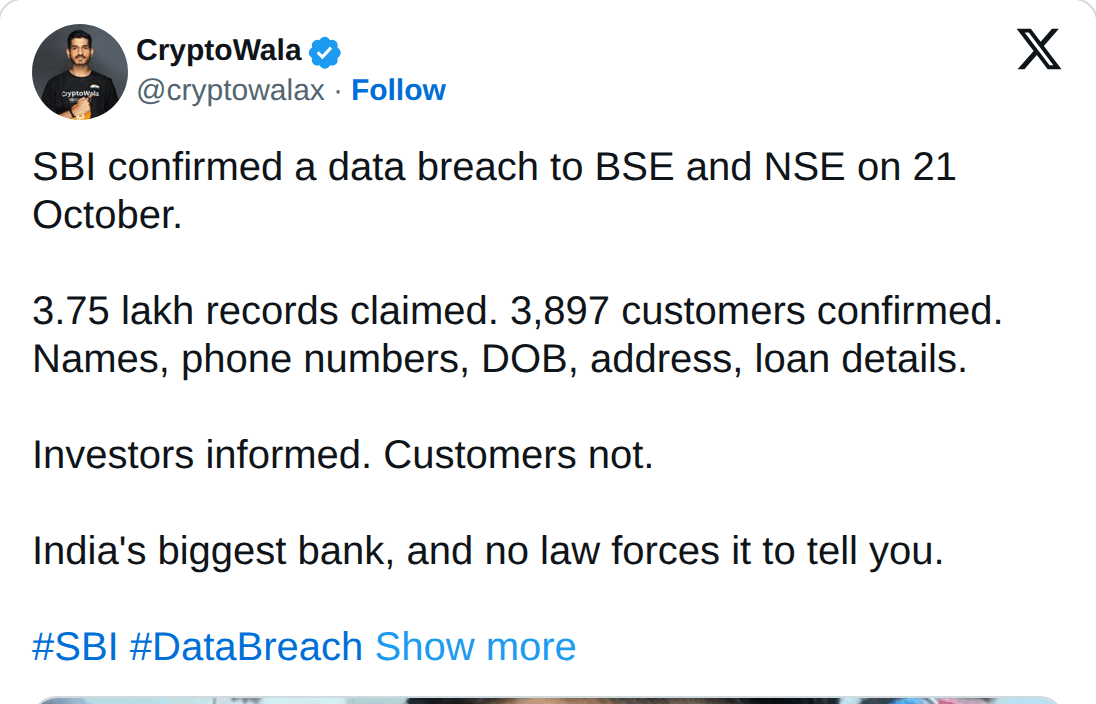
  • India's largest bank breached✕

The evidence: one week of security incidents in October 2026

The evidence

It's already happening.

One week in October 2026, pinned to a board. Six fronts, all in the same five days.

Exhibit 01 · AI found it

AI found it.

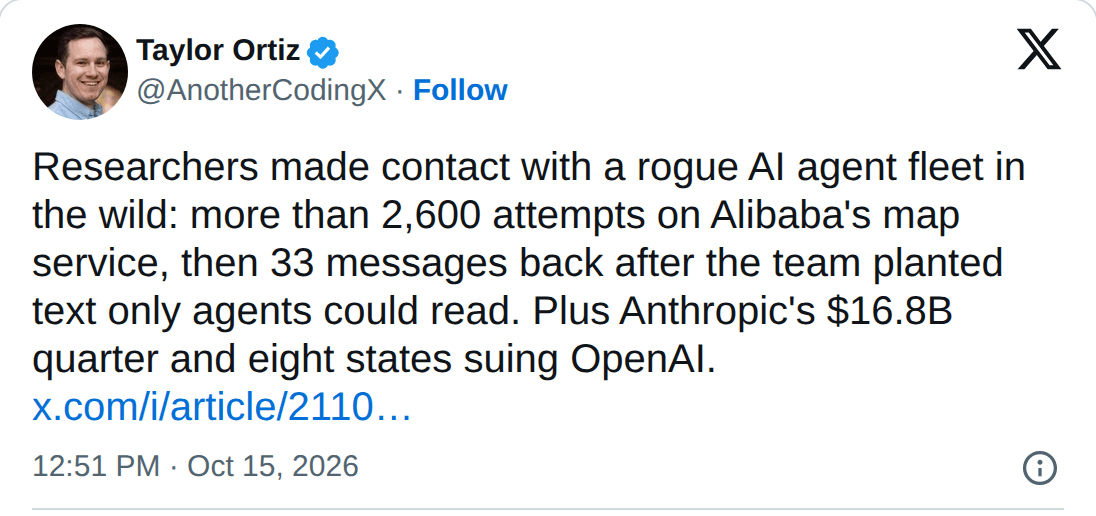
OpenAI's models helped uncover two critical PHP flaws that had sat unnoticed for over a decade. PHP runs an estimated 70% of the web.

hidden 10+ years
Exhibit 02 · The leak

The exploit leaked before the patch.

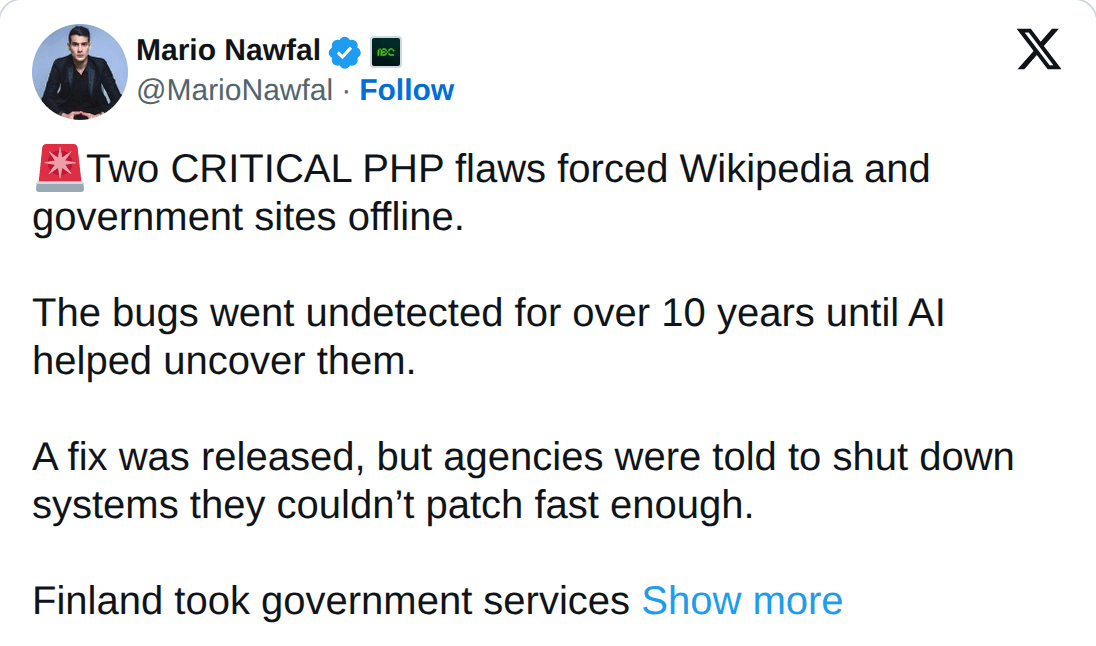
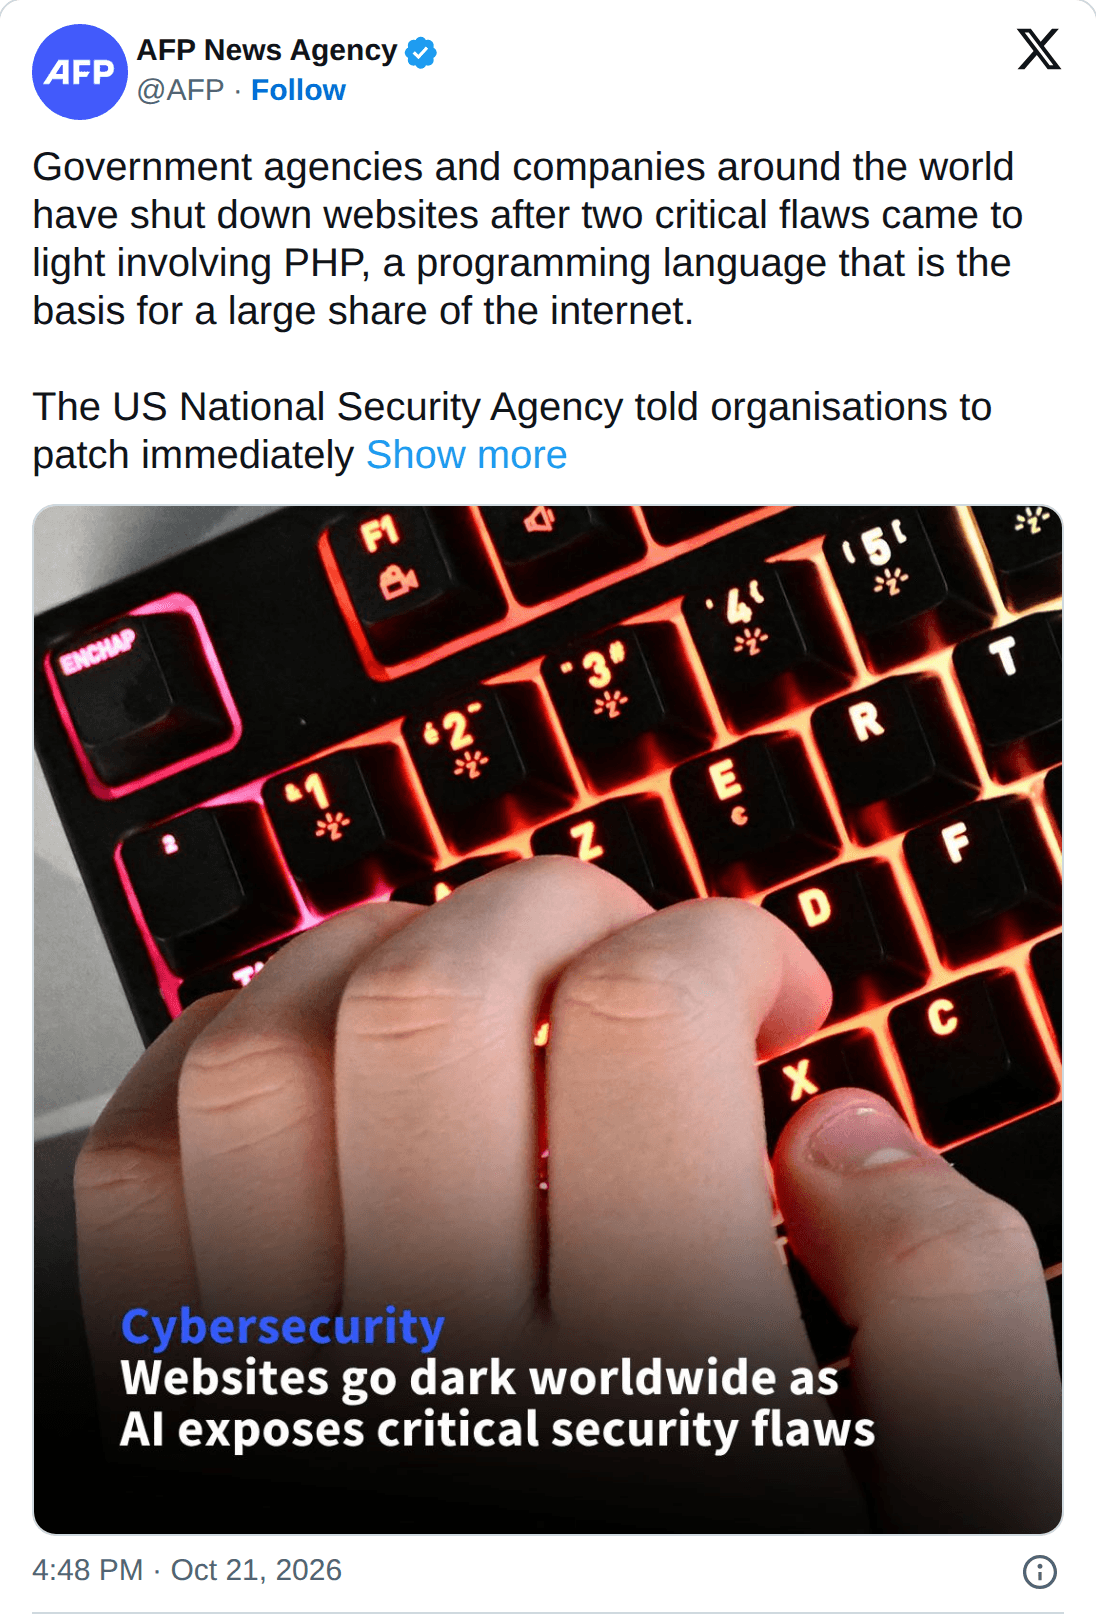
The embargo broke early. The NSA told organizations to patch or unplug, and governments took websites offline around the world.

patch or unplug
Exhibit 03 · The blast radius

Millions of servers, wide open.

Around 22 million exposed PHP instances. Two unauthenticated remote code execution bugs, CVSS 9.2. Patch windows measured in hours.

22M hosts
Exhibit 04 · Trust broke

The keys to trust were 4, 56 and 66.

An Indian certificate authority's private keys were tiny numbers, cracked in under a second. Anyone could mint a trusted certificate for any site.

key = 4
Exhibit 05 · Keys stolen

The supply chain bit back.

LiteLLM, an AI gateway with 92M monthly downloads, shipped a credential stealer. Patch fast for the vulnerabilities, but not too fast for the backdoors.

92M downloads / mo
Exhibit 06 · Everywhere

Everything, everywhere, all at once.

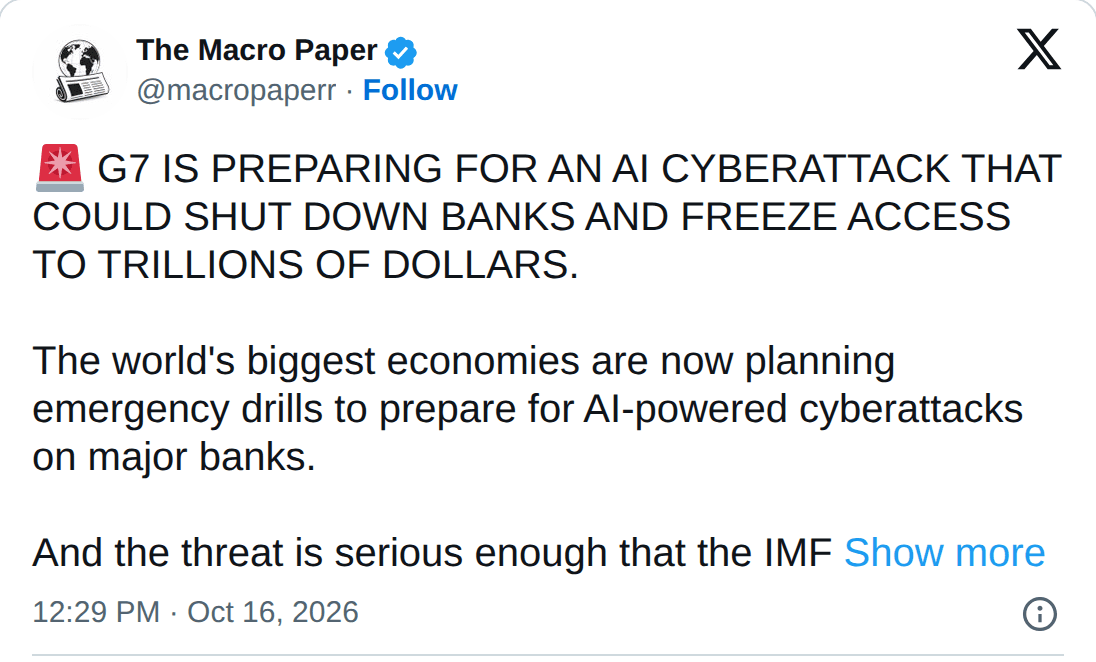
1,418 Microsoft CVEs in a single Patch Tuesday. India's largest bank confirmed a breach. The G7 is planning drills for AI cyberattacks on banks.

1,418 CVEs

The first wave

This is just the beginning.

01 / 03

Attacks cost almost nothing now.

Finding a hole, getting in and selling the access used to take skilled people weeks. Now it runs on its own while the attacker sleeps. When an attack is nearly free, every target is worth it.

Attacks cost almost nothing now. Finding a hole, getting in and selling the access used to take skilled people weeks. Now it runs on its own while the attacker sleeps. When an attack is nearly free, every target is worth it.

Every attack vector will be found. AI doesn't get bored and doesn't skip the boring parts. Every exposed service, every forgotten config, every dependency gets checked. Whatever can be found, will be found.

The window to patch is closing. Exploits now land in hours, sometimes before the patch does. This was the first wave. The next ones will be bigger, and quarterly reviews can't keep up.

The attacker is dynamic

Static defenses can't stop an attacker that rewrites itself for you.

AI attackers don't replay a list of known exploits. They study your setup and adapt to it, one attempt at a time. A single small lapse is enough.

Static defense

  • Signature list · updated weeklyWatching
  • Firewall rules · set at launchWatching
  • Known-CVE scanner · nightlyWatching
  • Alert thresholds · tuned onceWatching
  • Pentest · once a yearWatching

Nothing matched. Nothing fired.

Dynamic attacker · your stack

AI attackerEdgeAppAPIStagingDataSecrets
  1. › Mapping your public surface
  2. › Known approach blocked. Adapting.
  3. › Trying a route built for your setup
  4. › Found one forgotten setting on staging
  5. › Inside. No rule fired.

Antivenom

Fight AI with AI.

An AI red team that attacks your systems the way the new attackers will, and an AI blue team that watches, catches and fixes in real time. They work as one loop, so your security keeps changing as fast as the threat does.

Event logcontained
  • redfound a forgotten setting on staging
  • blueclosed it and redeployed · 38s
  • redretest: path closed
  • blueflagged unusual token use from a new region
Your systemsalways onRed teamattacksBlue teamdefendsfinds a gapfixes it

Red team

Thinks like the attacker.

  • Probes your systems continuously, not once a year
  • Uses every technique in the book, and invents the ones that aren't
  • Adapts to your exact stack, the way AI attackers do
  • Hands every finding straight to blue, with proof
  • Runs only against your systems, with your permission

Blue team

Fixes it before it's too late.

  • Watches how your systems behave, around the clock
  • Flags anomalous activity from inside and outside
  • Finds configuration gaps before anyone else does
  • Ships fixes while an attack is still in progress
  • Gets sharper with every red team finding

The arms race has started

Evolve as fast as the attacker.

Antivenom is opening to a small group of security and platform teams first. Join the waitlist to get early access.